Global companies and governments moved quickly to patch critical PHP vulnerabilities after cloud firms reported a surge in hacking attempts. Emergency shutdowns affected banking, airline, rail, tax and government services from Tokyo to Helsinki, according to Insurance Journal. The flaws, present in PHP for years and found using AI, prompted developers to urge immediate updates.
Cloudflare and Amazon reported millions of hacking attempts after details of the flaws became public. Some Japanese firms, including Tokio Marine Holdings and Mitsubishi UFJ Financial Group, suspended online services as a precaution. France's Orange and China’s Tencent Cloud also took steps to protect PHP-based systems. Finland’s Valtori said restoring services could take days or weeks, with no evidence of breaches so far.
The incident shows the deep reliance on ageing programming tools and the challenge of maintaining secure systems as complexity grows. Regulators and industry groups in Asia and Europe advised urgent updates, security reviews and enhanced monitoring. Smaller organisations face extra risk if they run outdated PHP versions without available security fixes.
Senior leaders in regulated sectors should review patch management processes and ensure that software dependencies are monitored and updated. The speed and scale of attempted exploits show the need for rapid response and regular system audits.
AM Best says commercial auto liability insurance in the US has seen claim costs rise by 6.4% annually over the past decade, outpacing average economic inflation of 2.8%. The ratings agency attributes this to social inflation, which it defines as the rising cost of claims above general inflation, driven by factors such as higher jury awards and broader definitions of liability.
Policy limits for commercial auto liability are typically $1 million, with claims above this threshold moving to umbrella policies. AM Best notes that, until 2018, umbrella pricing tracked closely with general liability pricing. As social inflation began to affect commercial auto claims, losses have increasingly spilled into umbrella coverages, pushing umbrella policy pricing higher and away from general liability trends.
This trend puts additional pressure on insurers’ underwriting strategies and risk models. Commercial policyholders may face higher premiums and stricter terms as insurers adjust to these cost increases. The report suggests continued monitoring of litigation trends and pricing responses across the sector.
Chubb CEO Evan Greenberg said the insurance sector should use its experience with past emerging risks to manage the growing issue of AI liability. Speaking on a third quarter earnings call, Greenberg described AI liability as a new and expanding exposure that has not yet been factored into casualty underwriting. He suggested the industry may need to develop a mix of coverage clarifications, exclusions and separate AI-related liability policies as the risk becomes clearer.
Greenberg noted that AI-related liability exposures will differ by business and sector, and that new underwriting and pricing methods will be needed to reflect this. He also raised the possibility of certification standards and best practices for AI use, which could help insurers assess and manage these risks. At Chubb, Greenberg said the company invests in governance and security for its own AI systems and data, using multiple layers of defence to protect against external threats.
For senior executives in regulated industries, the evolution of AI liability coverage will affect risk management, compliance and insurance costs. Insurers and clients should monitor developments in policy terms and industry standards as the market adapts to the risks posed by artificial intelligence.
Quest Diagnostics has reported unauthorised access to its Quanum LSM system, used by some clients to manage test orders and results. According to the company's filing with the U.S. Securities and Exchange Commission, Quest learned of the breach on 21 October and notified federal law enforcement. The company has started its cybersecurity response procedures and said the incident has not materially disrupted business operations so far.
The full extent of the breach is still being investigated, but Quest believes certain patient records were accessed without authorisation. This event follows a series of cyberattacks targeting the healthcare sector, including incidents involving medical device manufacturers and pharmaceutical suppliers.
For healthcare and insurance executives, the breach highlights persistent risks to patient data and operational continuity. It also raises questions about the adequacy of existing cybersecurity measures and the response protocols in regulated sectors.
The investigation's outcome will be watched closely, as further details may prompt changes in security standards and regulatory scrutiny across the industry.
European Union officials are considering tighter rules for insurers involved in unfunded significant risk transfers (SRTs) as part of a broader package to ease access to securitised finance. According to a note seen by Bloomberg, insurers would need to meet extra solvency standards if policymakers approve more lenient capital treatment for these products. The European Commission cited the 2008 AIG bailout as a cautionary example of the risks of unsecured credit protection.
The proposal would require insurers to maintain certain solvency ratios over three years, involve at least two protection providers per deal, and include provisions for replacing downgraded insurers. Supervisors would also assess banks’ and insurers’ concentration risks in SRTs. The European Insurance and Occupational Pensions Authority and the European Systemic Risk Board would be tasked with monitoring systemic exposures.
Unfunded SRTs leave banks reliant on insurers’ ability to pay claims, raising legal and liquidity risks. The capital treatment for banks depends on whether these protections are deemed ‘resilient’, affecting the risk floor applied. Insurers are expanding in this market, expecting to increase participation by 50% this year, according to an industry survey.
Banks such as Unicredit, BNP Paribas, and BBVA have recently completed unfunded SRT deals, while Credit Agricole is considering new transactions. The outcome of the EU’s deliberations will shape future market access and regulatory obligations for both banks and insurers.
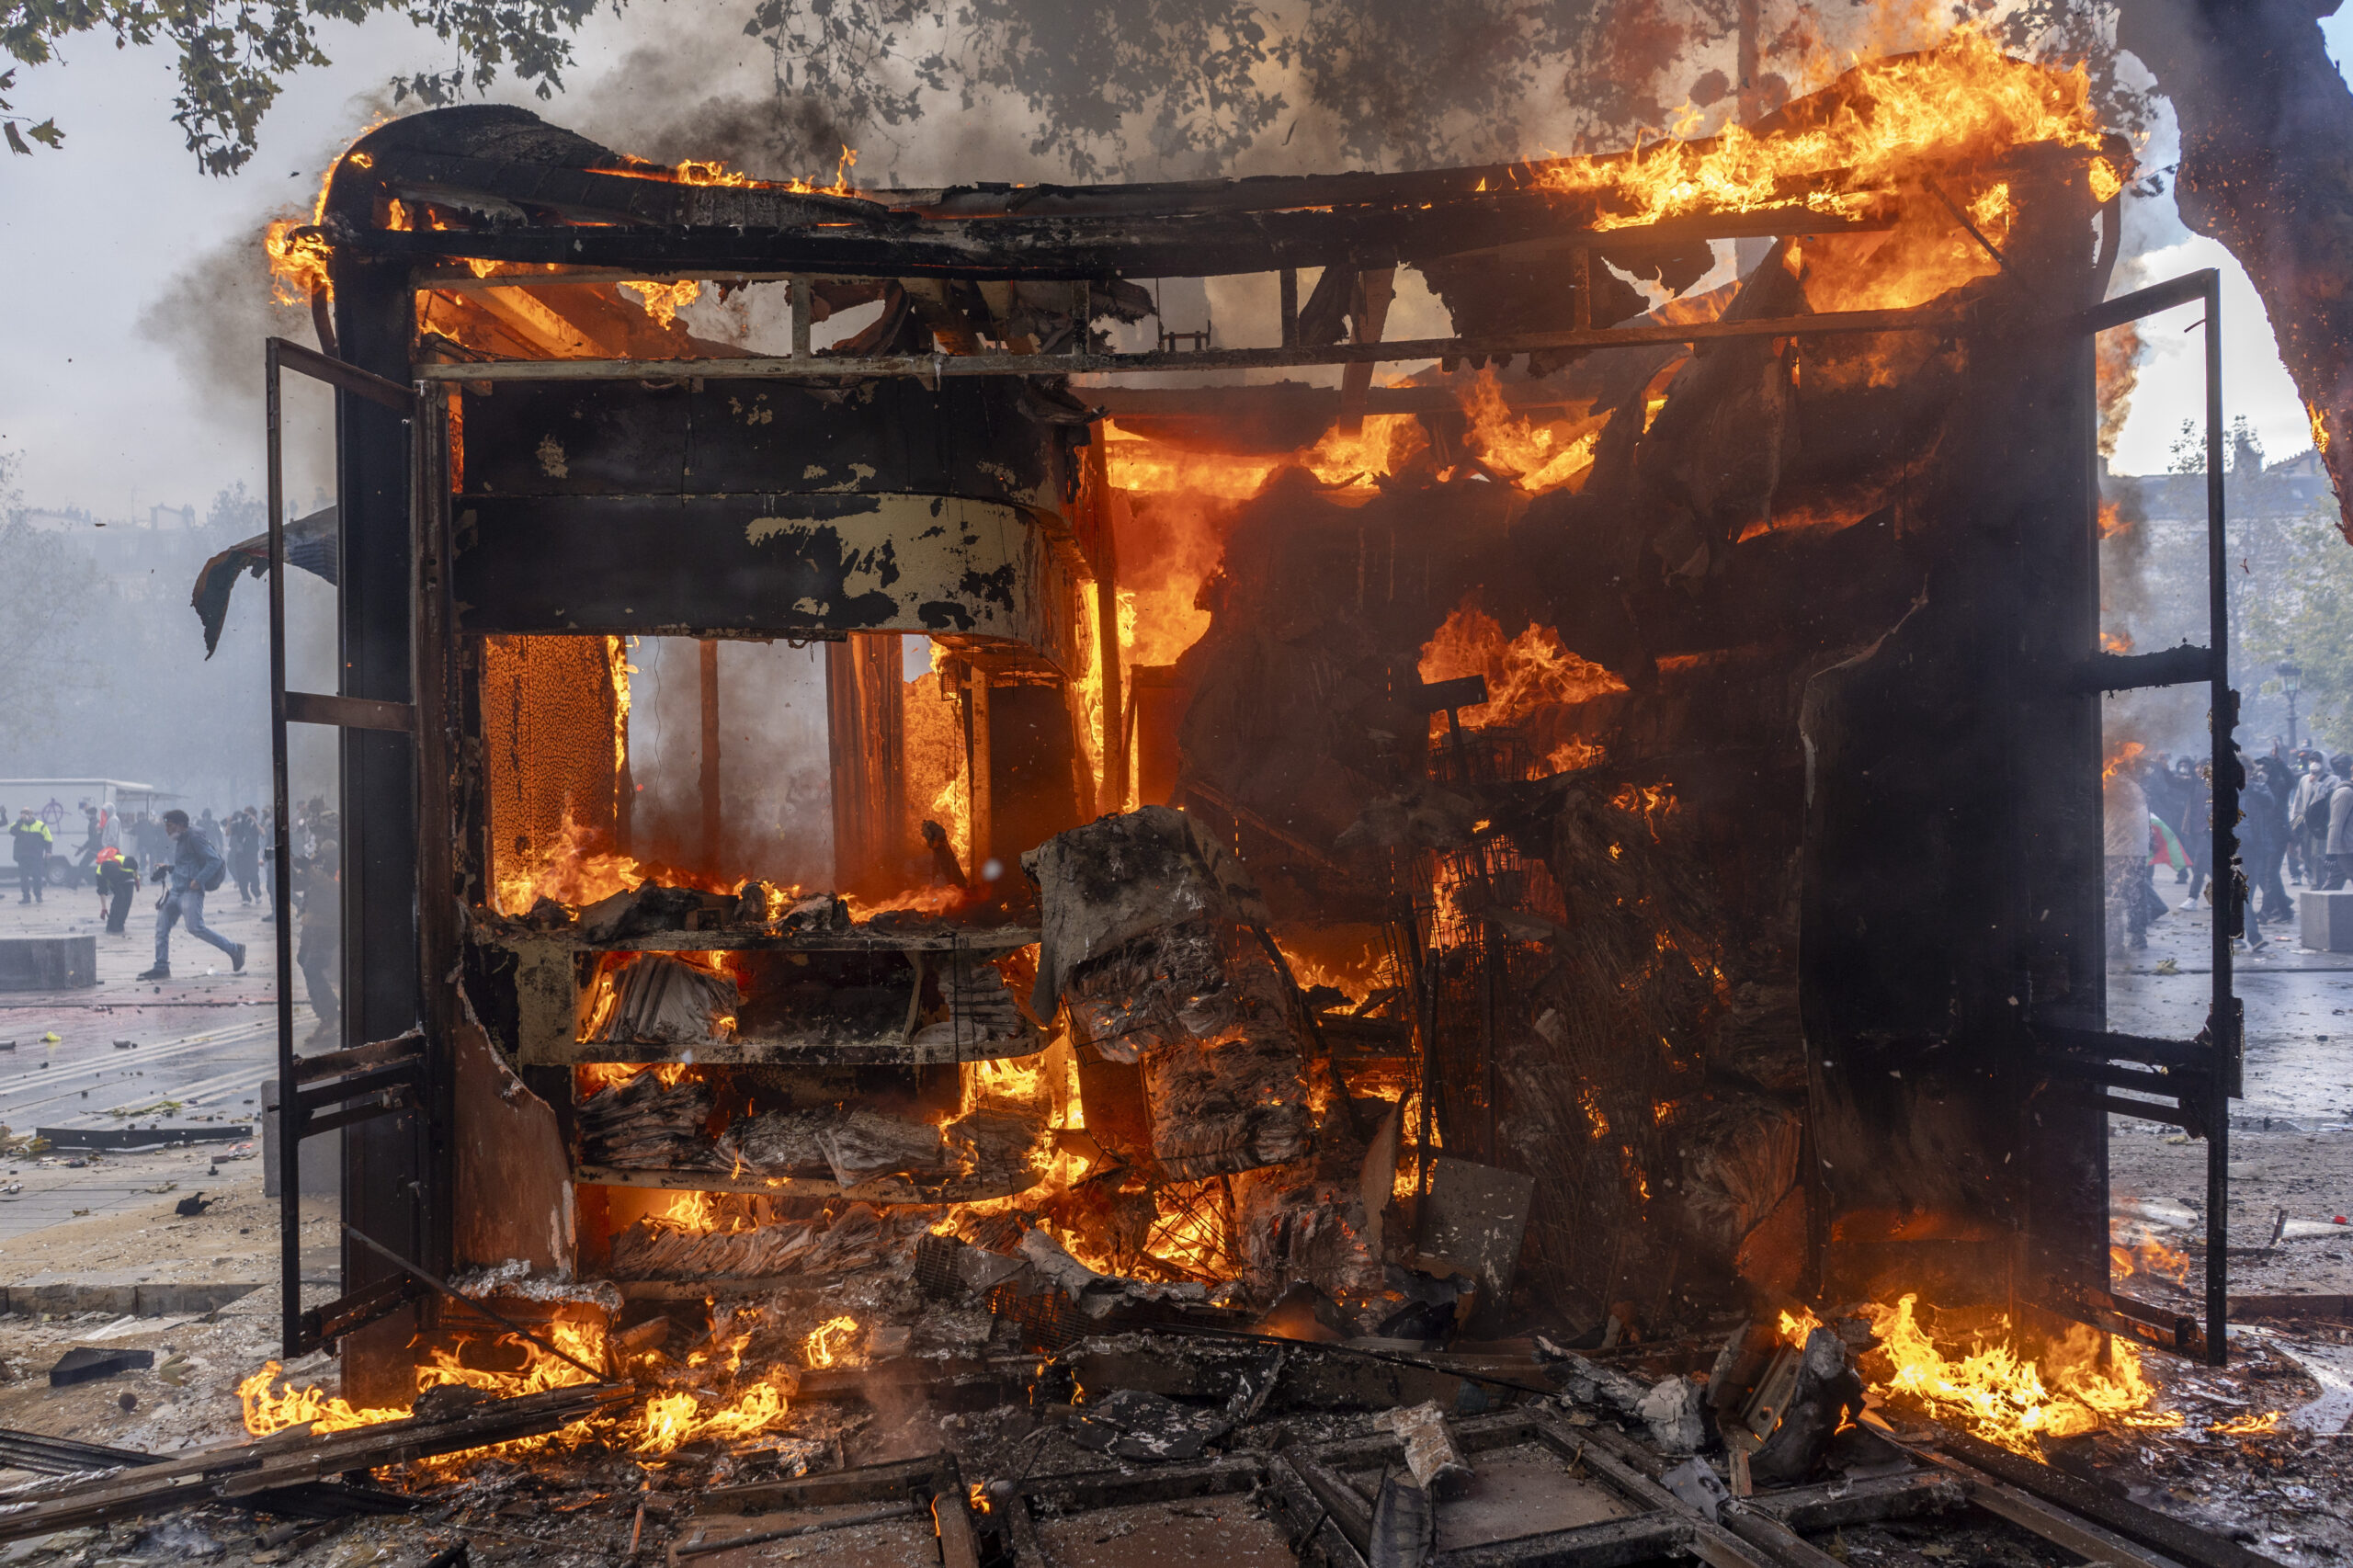
Recent street riots across France have caused widespread property damage, with insured losses estimated below €1.2 billion, according to DBRS Morningstar analysts. The unrest, which involved over half a million protesters and led to thousands of arrests, will test the effectiveness of current insurance arrangements just months before a new state-backed insurance framework is set to begin.
The forthcoming regime will introduce mandatory riot risk coverage in property insurance contracts, supported by a mutualisation mechanism managed by the French State through the CCR. This aims to help insurers manage systemic risks from civil unrest by transferring a significant share of qualifying losses to the public backstop. Until then, insurers remain dependent on a mix of private insurance, reinsurance, and potential state intervention.
DBRS Morningstar notes that the main concern for insurers is not the size of individual claims, but the aggregation of thousands of claims across multiple portfolios when unrest spreads. The estimated losses are expected to affect earnings but not threaten the capital positions or credit profiles of major French insurers.
Finance Minister Roland Lescure has announced support measures for affected businesses, and insurers such as AXA and BPCE Assurances have extended claim reporting deadlines to 30 days.
The Bank of England is discussing whether to include artificial intelligence as a central risk in its next system-wide exploratory scenario, according to sources familiar with the matter. The current exercise focuses on private markets and is set to conclude next year, but AI is rising on the regulatory agenda amid concerns over valuation bubbles, cyber risks, and the potential for AI-driven trading models to amplify market shocks.
Officials are concerned that AI agents used in trading could prompt herding behaviour, increasing volatility if models respond similarly to market events. There is also regulatory attention on the risk of AI exposing weaknesses in cyber defences and the possibility of an AI stock valuation bubble bursting with wider economic effects. The Bank's current scenario already includes some AI disruption, but officials say the scope of concern has widened since the exercise began.
Governor Andrew Bailey has said AI could boost growth but has also warned of its risks, particularly in cyber security. The Bank is still considering its options for the next stress test, with no final decision yet on whether AI will be the main focus.
Senior executives in banking and insurance should prepare for more scrutiny of AI risk management as regulators assess how technology could affect financial stability.
Cybercriminals are shifting from traditional ransomware and data breaches to more sophisticated fraud and business email compromise (BEC), according to executives at the NetDiligence Cyber Risk Summit. Christine Mapes of Travelers said that about 50% of the insurer’s cyber claims now involve financial fraud or BEC, with a 57% increase in such claims from the first half of 2025 to the first half of 2026. Claim severity has also risen by about 30% since 2023.
Tactics have evolved: attackers now use IT and bank fraud manipulation, often convincing victims to hand over access voluntarily. Artificial intelligence is fuelling this trend, enabling criminals to bypass language barriers and improve impersonation, according to Integreon’s Blake Feldman and Westfield Specialty’s Sara Trokan. Fraudsters increasingly combine email, audio, video, and social media to create convincing scams, sometimes tricking staff into making large payments.
While AI is also used to strengthen cyber defences, the panel agreed that basic verification processes remain effective. Lindsay Nickle of Constangy suggested that raising awareness and using low-tech checks, as was done with social engineering threats in the past, is still necessary.
Insurers and regulated firms should review their fraud controls and staff training as AI changes the threat profile. Monitoring new fraud trends and reinforcing verification procedures will be important as attackers adapt.
Hackers who infiltrated some of Japan's largest companies used the Chinese-developed AI tool ARTEX, which was also linked to recent breaches at South Korean banks, according to Tokyo-based GMO Cybersecurity by Ierae Inc. The attacks, launched from a single server infrastructure, targeted about 20 Japanese companies, including nine in the same industry, with e-commerce, finance, retail, logistics, media, education and marketing sectors among those affected.
Eight of the targeted firms have disclosed data leaks in the past two months, and the same group may be behind multiple incidents, said Daiki Fukumori, director at GMO Cybersecurity and a former Interpol investigator. The attackers appear to be running targeted, country- and industry-specific campaigns. The findings have been shared with law enforcement, and investigations are under way to determine if other countries are also being targeted.
The attacks have prompted calls from Japanese officials to strengthen cybersecurity measures. For regulated industries, the use of AI in cyberattacks raises the urgency for updated defences and cross-border cooperation. Boards and risk leaders should assess exposure to similar tools and review incident response plans.
Further disclosures from affected firms and possible regulatory guidance are likely as the investigation continues.