Cybersecurity Dive reports that the White House’s new AI task force does not include the Cybersecurity and Infrastructure Security Agency. Experts told the publication that this absence could make it harder for the group to work with critical infrastructure operators on AI security issues.
For banks, insurers and other regulated firms, the lack of direct input from the main US cybersecurity agency could mean less focus on sector-specific risks. Senior executives may need to monitor how the task force addresses security for vital systems and consider additional steps to protect their own operations.
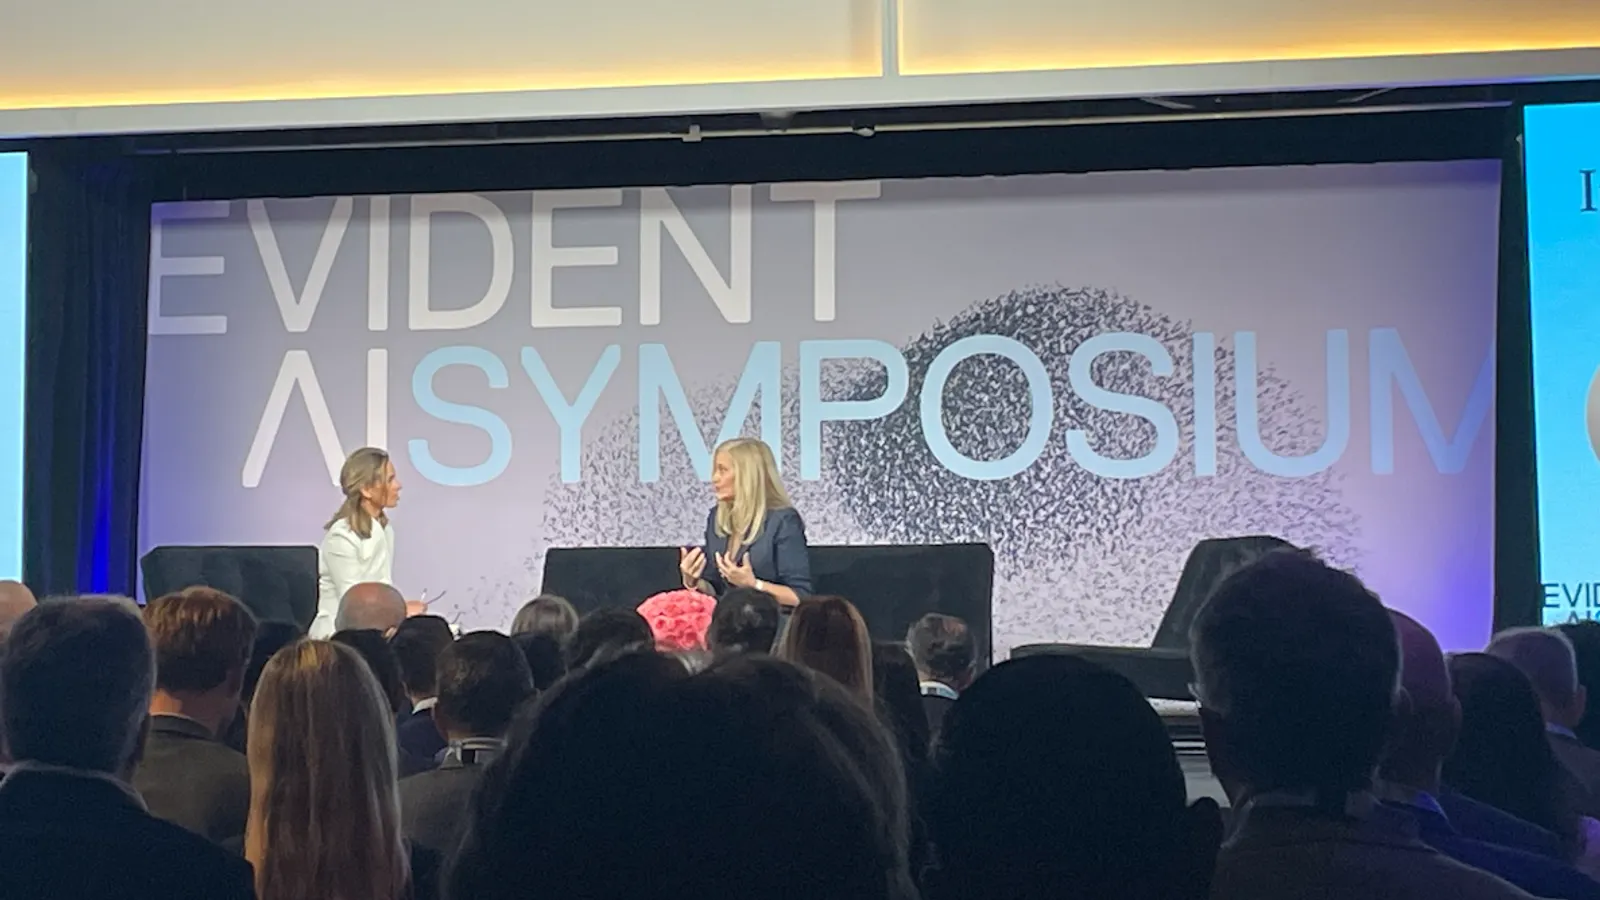
JPMorgan Chase and Goldman Sachs are placing security at the centre of their AI strategies, according to Cybersecurity Dive. JPMorgan Chase Global CIO Lori Beer said, “This is one of the most important times to make sure you are appropriately balancing risk and innovation.”
This focus signals that major banks see risk management as essential when adopting AI. For regulated firms, the message is clear: security must be considered from the outset in any AI project, not as an afterthought.
Cybersecurity Dive reports that the insurance industry is concerned a systemic cyber event linked to the PHP2Shell vulnerability could trigger billions in claims, surpassing what current risk models predict.
This raises questions for insurers and risk managers about their exposure to large-scale cyber incidents. Firms may need to reassess their modelling and risk assumptions to prepare for the possibility of unanticipated losses from widespread vulnerabilities.
Cybersecurity Dive reports that PwC, a major professional services firm, confirmed a ransomware actor accessed its learning records through a breach on a vendor site. The incident has been publicly claimed by a known ransomware group, according to the publication.
This incident draws attention to the risks posed by third-party vendors in handling sensitive data. For banks, insurers, and healthcare organisations, the breach shows the need for strong oversight of external partners and clear protocols for responding to cyber incidents.
A new report cited by Cybersecurity Dive says AI-powered attacks and hidden supply-chain weaknesses are making insurers’ work more difficult. The report finds that while large businesses are filing fewer cybersecurity insurance claims, the claims themselves are becoming more expensive to resolve.
This shift matters for regulated firms because insurers may respond by raising premiums or imposing stricter coverage terms. Boards and risk managers should expect more scrutiny of cyber risk controls and supply-chain due diligence in future renewals.