Anthropic, a San Francisco AI company, publicly accused three Chinese AI labs — DeepSeek, Moonshot AI, and MiniMax — of launching large-scale, coordinated campaigns using approximately 24,000 fraudulent accounts to extract capabilities from its Claude AI models. These labs generated over 16 million interactions with Claude, violating Anthropic's terms of service and regional restrictions, with the intent to shortcut years of research investment through a technique called distillation. This process involves extracting knowledge from a larger AI (the "teacher") to train a smaller one (the "student") by using the teacher’s outputs instead of raw data. While distillation is a legitimate training method, Anthropic claims these labs weaponized it by systematically siphoning AI capabilities at scale. The revelations heighten tensions amid U.S.-China debates over AI chip export controls, with Anthropic framing the issue as a national security risk rather than just intellectual property theft. The labs allegedly employed sophisticated proxy networks to bypass restrictions, and Anthropic is calling for industry-wide collaboration to tackle this escalating threat. The company has made technological, verification, and protective adjustments in response but stresses that collective action is required to safeguard frontier AI models.

Traditional ETL tools like dbt and Fivetran focus on preparing stable, structured data for reporting and dashboards. However, AI applications require a different approach, as they must handle messy, evolving operational data in real-time for accurate model inference. Empromptu identifies this need as "inference integrity" rather than the conventional "reporting integrity." Their "golden pipeline" solution integrates data normalization directly into the AI workflow, cutting what normally takes weeks of manual engineering down to under an hour. This automated layer ingests data from diverse sources, cleans and structures it, enriches and labels records, and applies governance and compliance safeguards. Crucially, golden pipelines continuously evaluate data transformations against how models perform in production, ensuring accuracy and trustworthiness. This method is designed specifically for mid-market and enterprise clients in regulated fields like fintech, healthcare, and legal tech. A notable real-world success is VOW, an event platform that leveraged golden pipelines to automate complex, fast-moving event data preparation, achieving a level of precision unattainable with previous manual methods or other AI providers. While golden pipelines excel in environments where integrated AI apps and smooth, reliable data prep are vital, they may be less fitting for mature data engineering teams or standalone AI model development. The core value lies in removing the delays and errors that occur when dataset preparation and AI application building are treated as separate processes, thus accelerating AI deployment at scale.

While AI is often seen as automating human work, it still heavily depends on human involvement, especially in training models through reinforcement learning from human feedback (RLHF). Rapidata introduces a groundbreaking platform that transforms this process by distributing review tasks to millions of mobile app users globally in place of traditional ads, allowing instant feedback to AI labs. This dramatically accelerates AI model development from months to just days.
Founded by Jason Corkill, Rapidata addresses the long-standing issue of slow, fragmented human annotation workflows by leveraging existing mobile app audiences to collect high-quality, rapid feedback. The platform supports massive scale and speed with features like parallel processing of up to 1.5 million annotations per hour, global user reach, and quality control via trust profiles — all while maintaining user anonymity.
This innovation integrates human insights directly into AI training loops on GPUs in near real-time, enabling "online RLHF". This reduces delays, improves model authenticity, and helps AI systems better capture subjective nuances such as taste and cultural context. Industry leaders acknowledge Rapidata as critical infrastructure for the next generation of AI, ensuring that human judgment remains a scalable, dynamic part of AI progress.
With an $8.5 million seed round and partnerships spanning popular apps, Rapidata is poised to shift AI development from static cycles to continuous, evolving feedback, bridging the gap between silicon-based AI and society’s complex human experience.

Late last year, Google temporarily claimed the title of the world’s most powerful AI model with Gemini 3 Pro, only to be quickly overtaken by competitors OpenAI and Anthropic. Now, Google is back on top with Gemini 3.1 Pro, an enhanced model designed for complex tasks that demand deep planning and synthesis, targeting scientific, research, and engineering sectors.
Independent evaluation shows Gemini 3.1 Pro leads in AI performance with a remarkable leap in logical reasoning benchmarks, achieving a verified 77.1% on ARC-AGI-2 — more than twice the previous model’s capability. The model also excels in scientific knowledge, coding, and multimodal understanding with high scores across respective benchmarks.
Among practical innovations, Gemini 3.1 Pro introduces "vibe-coded" animated SVGs generated directly from text prompts, offering scalable, high-quality visuals ideal for enterprise applications. Demonstrations include live aerospace dashboards, interactive 3D designs, and creative web designs inspired by literary themes.
Enterprise users report significant gains in model reliability and efficiency. Pricing remains consistent with Gemini 3 Pro, providing substantial performance improvements without increased costs for API users. Available through Google’s Vertex Studio and Gemini API, Gemini 3.1 Pro operates on a commercial SaaS model, ensuring secure, grounded reasoning for business use.
This release underscores Google’s commitment to AI models that not only predict but deeply "think" through challenges, setting a new standard in the AI race.
Customer experience (CX) platforms handle billions of unstructured interactions annually, feeding AI engines that automate workflows connecting payroll, CRM, and payment systems. However, SOC tools typically don't inspect the data ingested by these CX AI engines, creating exploitable blind spots. In a notable breach in August 2025, attackers compromised Salesloft’s GitHub and stole Drift chatbot OAuth tokens, gaining unauthorized access across 700+ organizations’ Salesforce environments, including major companies like Cloudflare and Palo Alto Networks, without deploying malware.
Six critical security gaps enable these attacks: traditional DLP tools can't detect sensitive sentiment data in API calls; expired API tokens remain active; public input channels lack bot mitigation; lateral movement exploits approved API calls; non-technical users hold unmonitored admin privileges; and unmasked PII enters databases through open-text feedback. These issues reflect a lack of tailored SaaS security posture management for CX platforms, unlike mature solutions for Salesforce or ServiceNow.
Security teams are adapting by extending SSPM, API security gateways, and CASB controls to CX platforms, but comprehensive protection needs real-time monitoring, configuration visibility, and automated policy enforcement specific to CX data flows. The first purpose-built integration combining posture management with the CX layer is emerging through partnerships like CrowdStrike’s Falcon Shield and Qualtrics XM Platform.
Beyond technical impact, poisoned AI-driven business decisions create an untracked blast radius affecting CIOs, CISOs, and business owners. Prioritizing audits for active tokens and validating integrations promptly is critical, as AI-driven threats advance faster than traditional review cycles.
In the realm of AI development, especially within complex fields like law, accuracy is crucial but insufficient on its own. LexisNexis has advanced beyond basic retrieval-augmented generation (RAG) methods to introduce graph RAG and innovative AI agents that critically assess and improve their own outputs. According to Min Chen, LexisNexis' SVP and chief AI officer, perfect AI is unattainable; the focus instead is on managing uncertainty to deliver consistent, high-quality results. To enhance reliability, the team evaluates AI responses on multiple sub-metrics such as authority, citation accuracy, hallucination rates, and completeness, ensuring answers fully address multifaceted legal inquiries. Their legal AI tools, like Lexis+ AI and Protégé, incorporate hybrid vector searches and knowledge graph layers to provide authoritative legal content and automate complex tasks with planner and reflection agents. This approach fosters a collaborative future where AI and human expertise work together to elevate legal research and drafting.

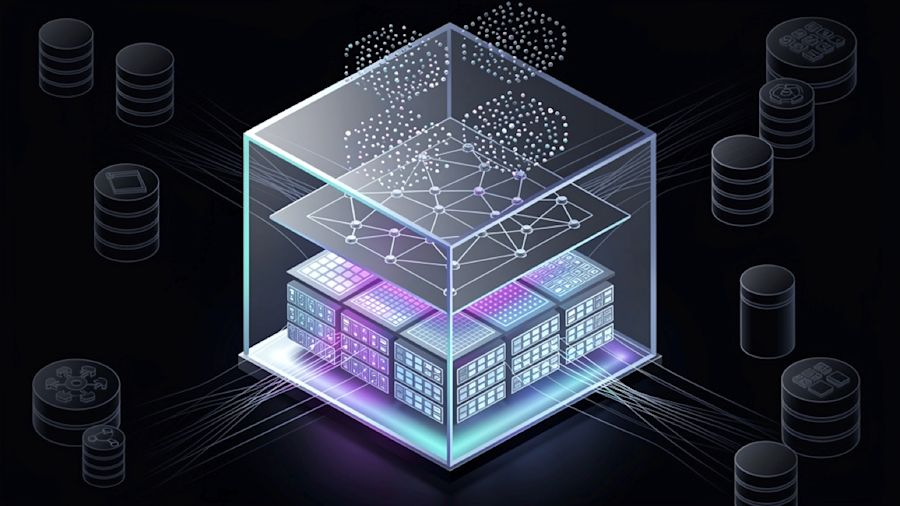
Creating retrieval-augmented generation (RAG) systems for AI agents typically requires juggling several distinct databases for structured data, vectors, and graph information. This multi-layered approach often leads to synchronization challenges and performance issues, especially as AI agents increasingly rely on contextual memory for better interaction. SurrealDB 3.0 addresses these challenges by integrating agent memory, business logic, and various data forms into a single Rust-native database engine, eliminating the need for multiple systems. The database enables transactional handling of vector searches, graph traversals, and relational queries simultaneously, ensuring consistency and real-time updates across distributed nodes without caching or read replicas. SurrealDB’s plugin system empowers developers to define and run memory-building logic inside the database, facilitating complex queries that seamlessly combine semantic, graph, and structured data. With over 2.3 million downloads and growing adoption in industries from automotive to retail, SurrealDB offers a streamlined alternative to traditional RAG stacks, significantly reducing development times from months to days when working with multi-modal data types.
OpenAI has announced the acquisition of OpenClaw, the open-source AI agent that has recently gained significant developer attention. Peter Steinberger, OpenClaw's creator, will join OpenAI to advance AI agents that can autonomously complete tasks, rather than just engage in conversation. The OpenClaw project will continue as an independent foundation with OpenAI sponsorship. This acquisition signals a shift in AI from conversational models to autonomous task-performing agents capable of browsing, coding, and acting on user behalf. OpenClaw stood out by integrating multiple capabilities including tool access, code execution, and messaging platform integration, fostering rapid adoption among developers. Despite security concerns and earlier legal conflicts with Anthropic, OpenClaw grew viral due to its bold approach and public development. Industry leaders note that the future of AI interfaces may come from boundary-pushing independent projects rather than established labs. IT and enterprise leaders should prepare for a landscape where "safe" autonomous agents become key. However, questions remain about whether OpenClaw will retain its open-source spirit under OpenAI's control. Steinberger aims to create an agent accessible to everyone, signaling a new era in AI use and development.
Developers often run OpenClaw on corporate laptops, inadvertently granting it unrestricted shell access and permissions for services like Slack, Gmail, and SharePoint. Recent security incidents reveal vulnerabilities such as CVE-2026-25253 and CVE-2026-25157 that allow attackers to exploit OpenClaw for remote code execution and credential theft. Public exposure of OpenClaw instances and its social network Moltbook has led to massive credential leaks, highlighting the risk of direct local installation. To counter this, Cloudflare's Moltworker framework offers a safer alternative by deploying OpenClaw within ephemeral, isolated containers that provide encrypted persistence and Zero Trust authentication, greatly reducing the attack surface and preventing persistent credential compromise. Setting up a sandbox environment typically takes an afternoon and costs significantly less than dedicated hardware, while enabling secure evaluation and adversarial testing without risking production data. Organizations are advised to use throwaway identities and test isolated environments before wider deployment to ensure robust credential handling and confirm sandbox boundaries hold in real use cases.
Large organizations often struggle to hold productive real-time conversations because ideal group sizes for discussion are small, yet most teams have hundreds or thousands of members. Traditional polls and surveys don't facilitate true deliberation or mutual understanding, treating people as mere data points instead of thoughtful contributors. A new technology, Hyperchat AI, inspired by swarm intelligence and powered by AI agents called "conversational surrogates," enables large groups to break into small discussion groups and weave their insights together in real time. This technology was tested with 110 Super Bowl viewers debating which ad was most effective, converging on consensus in just 10 minutes with statistically significant results. Hyperchat AI allows large teams to brainstorm, debate, prioritize, and solve problems collaboratively and efficiently, improving speed, accuracy, and buy-in on decisions.