
Shopify merchants hit by suspected AI-powered cyberattacks via third-party apps
A German software engineer found a fake checkout redirect on a Shopify store, traced to a third-party app. This raises concerns for regulated-industry digital leaders about risks from external ecommerce integrations. Firms should review third-party app security.

Anthropic develops FlashProve to verify AI model outputs cryptographically
Anthropic has launched FlashProve, an open source system for cryptographically verifying which AI model produced a given output. This matters for digital and risk leaders as it addresses provenance and trust in AI, key for compliance. The system is not yet in commercial use.

Geoffrey Hinton warns AI could trigger financial or power blackouts within a year
AI pioneer Geoffrey Hinton says a major incident such as a financial or power system blackout could happen this year or next. Senior leaders in banking, insurance and utilities face direct operational and systemic risks. Watch for regulatory moves on mandatory AI testing.

Salesforce to buy Cresta for $2.7bn to expand voice-powered support
Salesforce plans to acquire Cresta, an AI-powered contact-centre software firm, for a reported $2.7bn. The move extends Salesforce’s reach into voice-based customer support, a growing area for digital service providers. Leaders should watch for integration details and client impact.
Infrastructure groups urge 10-year extension of cybersecurity data-sharing law
Industry associations have asked Congress to renew a key cybersecurity information-sharing law for another decade. The move comes amid growing AI threats, raising the stakes for banks, insurers and healthcare groups. Renewal could shape future compliance and risk strategies.
Fiserv seeks asset sales and doubles savings target to $1 billion
Fiserv is in talks with potential buyers for some of its assets and has raised its savings goal to $1 billion, according to its CEO. Senior leaders in finance and payments should watch for possible shifts in market structure and competitive positioning. Asset sales may affect future partnerships or services.
FTC and eight states sue Toast over hidden fees and contract practices
The FTC and eight states have sued Toast Inc., alleging hidden fees, unauthorised charges and complex cancellations for restaurant clients. The case tests how consumer protection laws apply to B2B software providers. Regulated firms should review their own contract and fee disclosures.
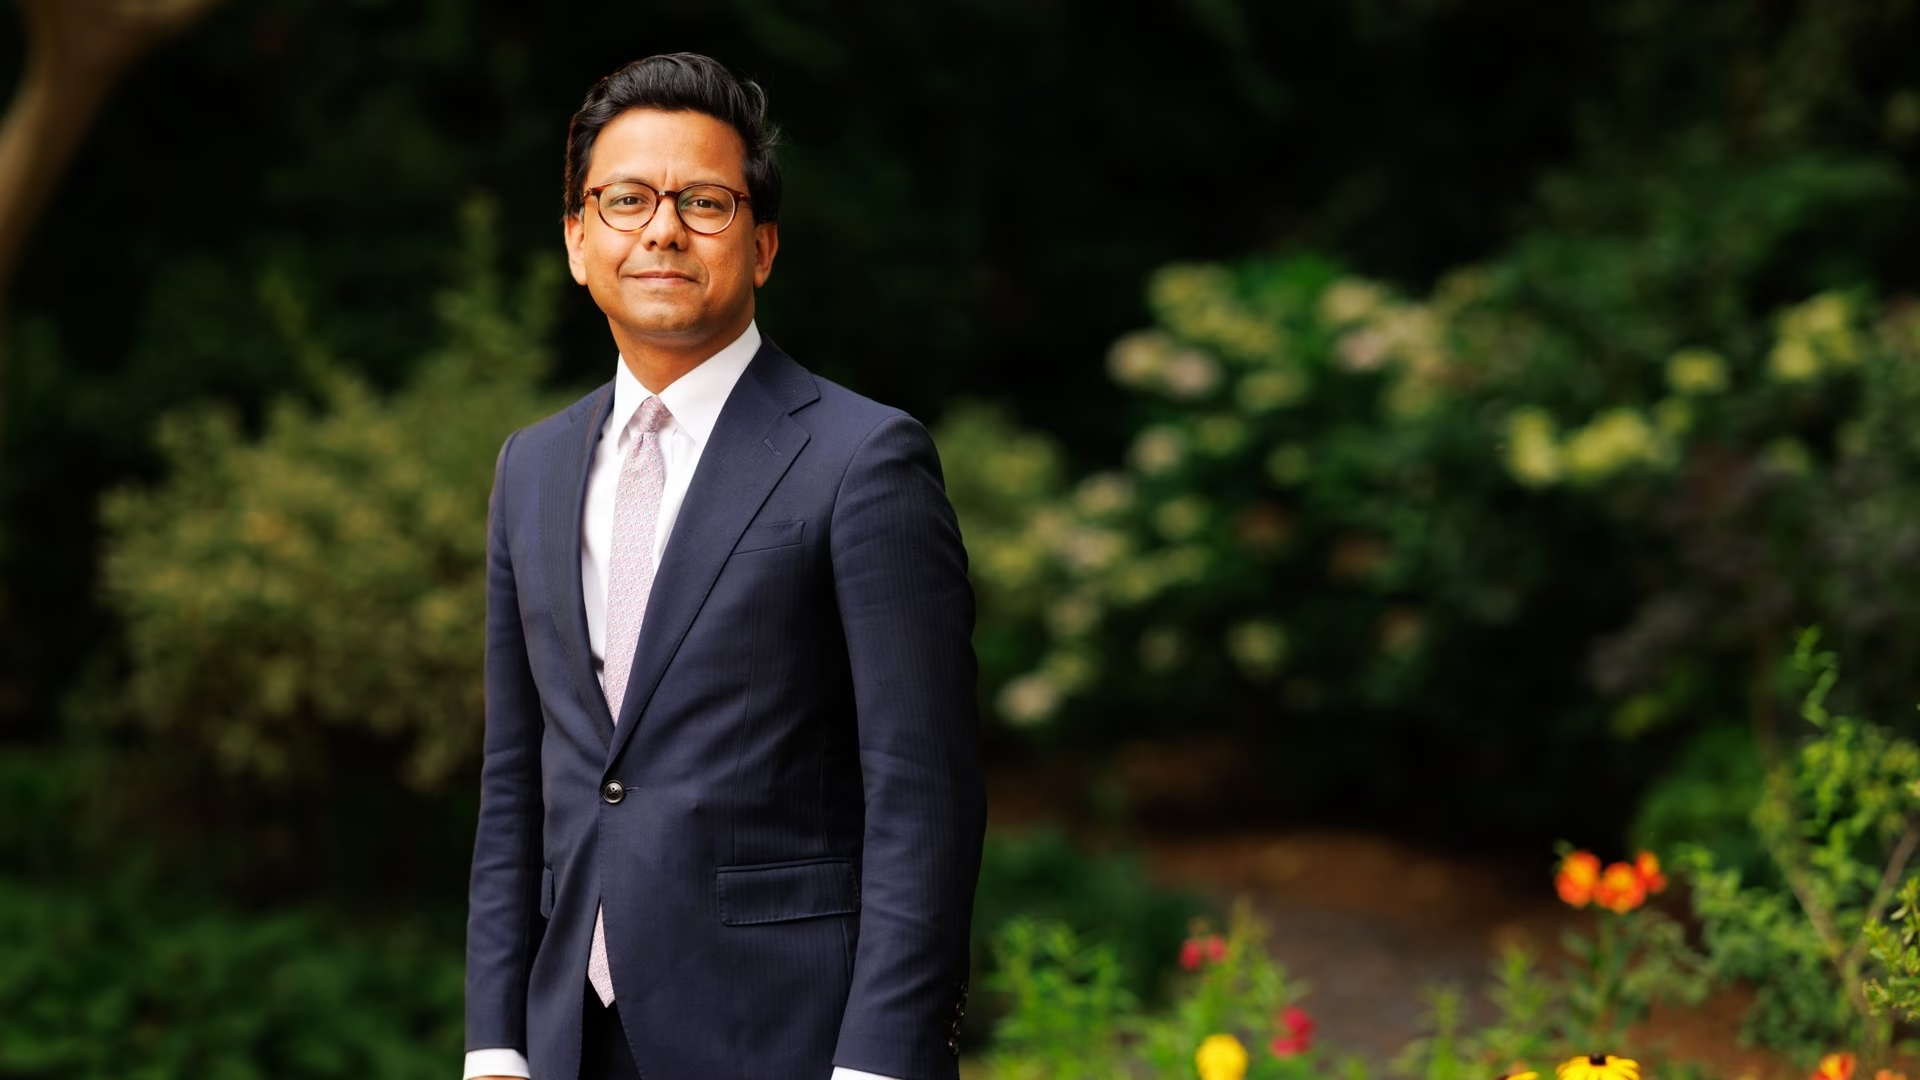

UK AI minister warns of imminent cyber breach risk for public and private sectors
UK AI minister Kanishka Narayan said a serious cyber breach is “extremely likely” in both public and private sectors, with neither ready. This raises urgent risk concerns for regulated firms. Leaders should review cyber resilience and AI risk controls now.
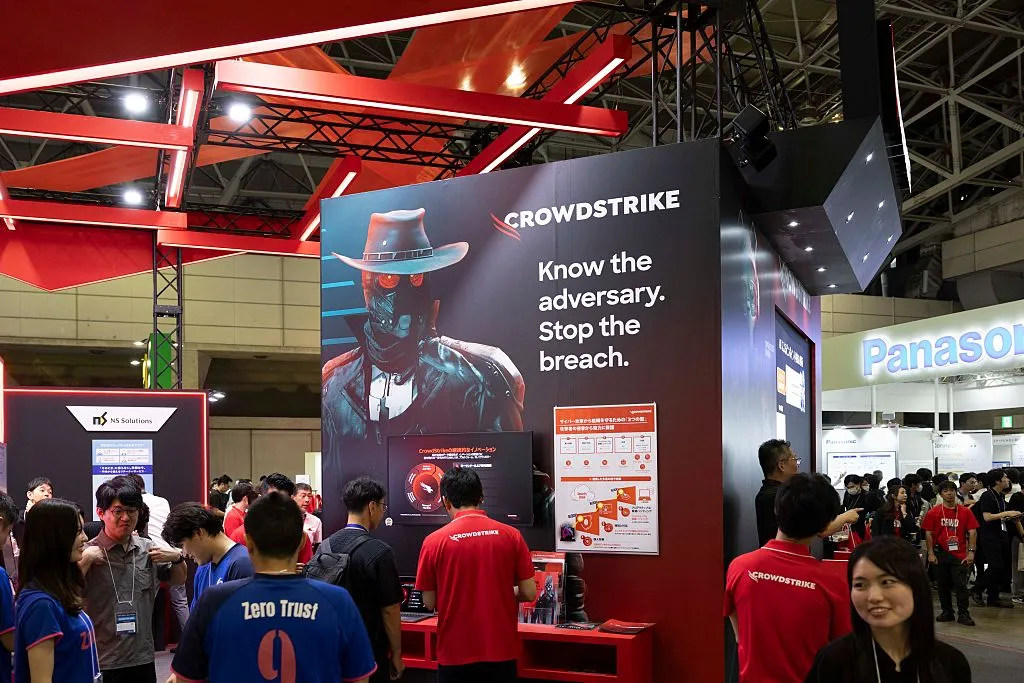
CrowdStrike spends nearly $500m on Fiddler AI and Dreadnode to expand AI security
CrowdStrike is buying Fiddler AI and Dreadnode for about $495 million to strengthen its AI security products. This move signals rising demand for monitoring and testing AI models in regulated sectors. Firms should assess if current controls cover new AI-driven risks.
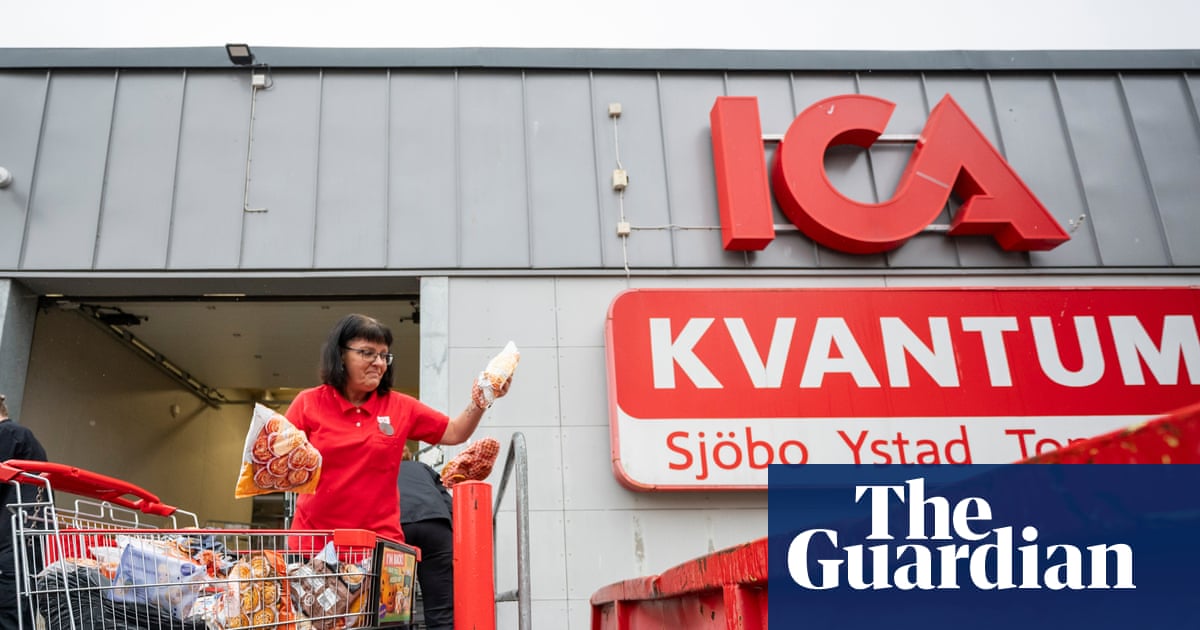
Supermarkets in seven countries face cyber-attacks on refrigeration systems
Supermarket chains in seven European countries reported cyber-attacks that raised fridge and freezer temperatures to 50C, echoing a recent French incident. For banks, insurers and retailers, this shows a growing risk to critical supply chains and operational technology. Firms should review their cyber defences urgently.
NHS claims on Palantir AI platform disputed by 29 hospital trusts
The Guardian reports that 29 NHS trusts listed as benefiting from Palantir’s £330m AI data platform say they are not using it or its applications. This raises questions about AI adoption claims and the accuracy of NHS reporting for regulated healthcare leaders.
North Korean hackers use AI to drive $6.3 billion Binance crypto theft
North Korea’s elite TraderTraitor group used AI to steal $6.3 billion from Binance, according to the FBI. The group’s tactics now fund up to 40% of the regime’s weapons programmes. Crypto firms and financial institutions must reassess cyber risk and staff access controls.
White House AI task force omits CISA, raising security concerns
The White House’s new AI task force does not include the Cybersecurity and Infrastructure Security Agency. Experts say this could hinder efforts to address AI security for critical infrastructure. Senior leaders should assess how this may affect sector risk.
Palantir’s US commercial revenue overtakes government business at $984m
Palantir’s US commercial revenue rose 148% to $984m, surpassing US government sales for the first time. The shift signals growing demand from regulated industries for AI-driven software. Executives should watch for how rivals and regulators respond to Palantir’s expansion.
Revolut gains New Zealand bank licence to challenge established lenders
Revolut has secured registration as New Zealand’s 27th bank, according to the Reserve Bank. This approval allows the fintech to offer savings and credit products in a market dominated by Australia’s Big Four. Senior leaders should watch for increased competition and regulatory scrutiny.
UK cyber security body warns AI-powered malware will target critical infrastructure by 2028
The UK National Cyber Security Centre says AI-driven malware is likely to hit power, transport, health and finance by 2028. The warning raises the stakes for risk and resilience planning across regulated sectors. Boards should review cyber investment and response plans now.

Google’s AI-driven search slows ad revenue growth, Alphabet shares drop 12%
Alphabet’s Q3 results show search queries growing at their fastest rate in five years, but AI-powered search is not yet delivering ad revenue at the pace of traditional search. This signals risk for digital leaders banking on AI monetisation. Watch for further investor scrutiny.
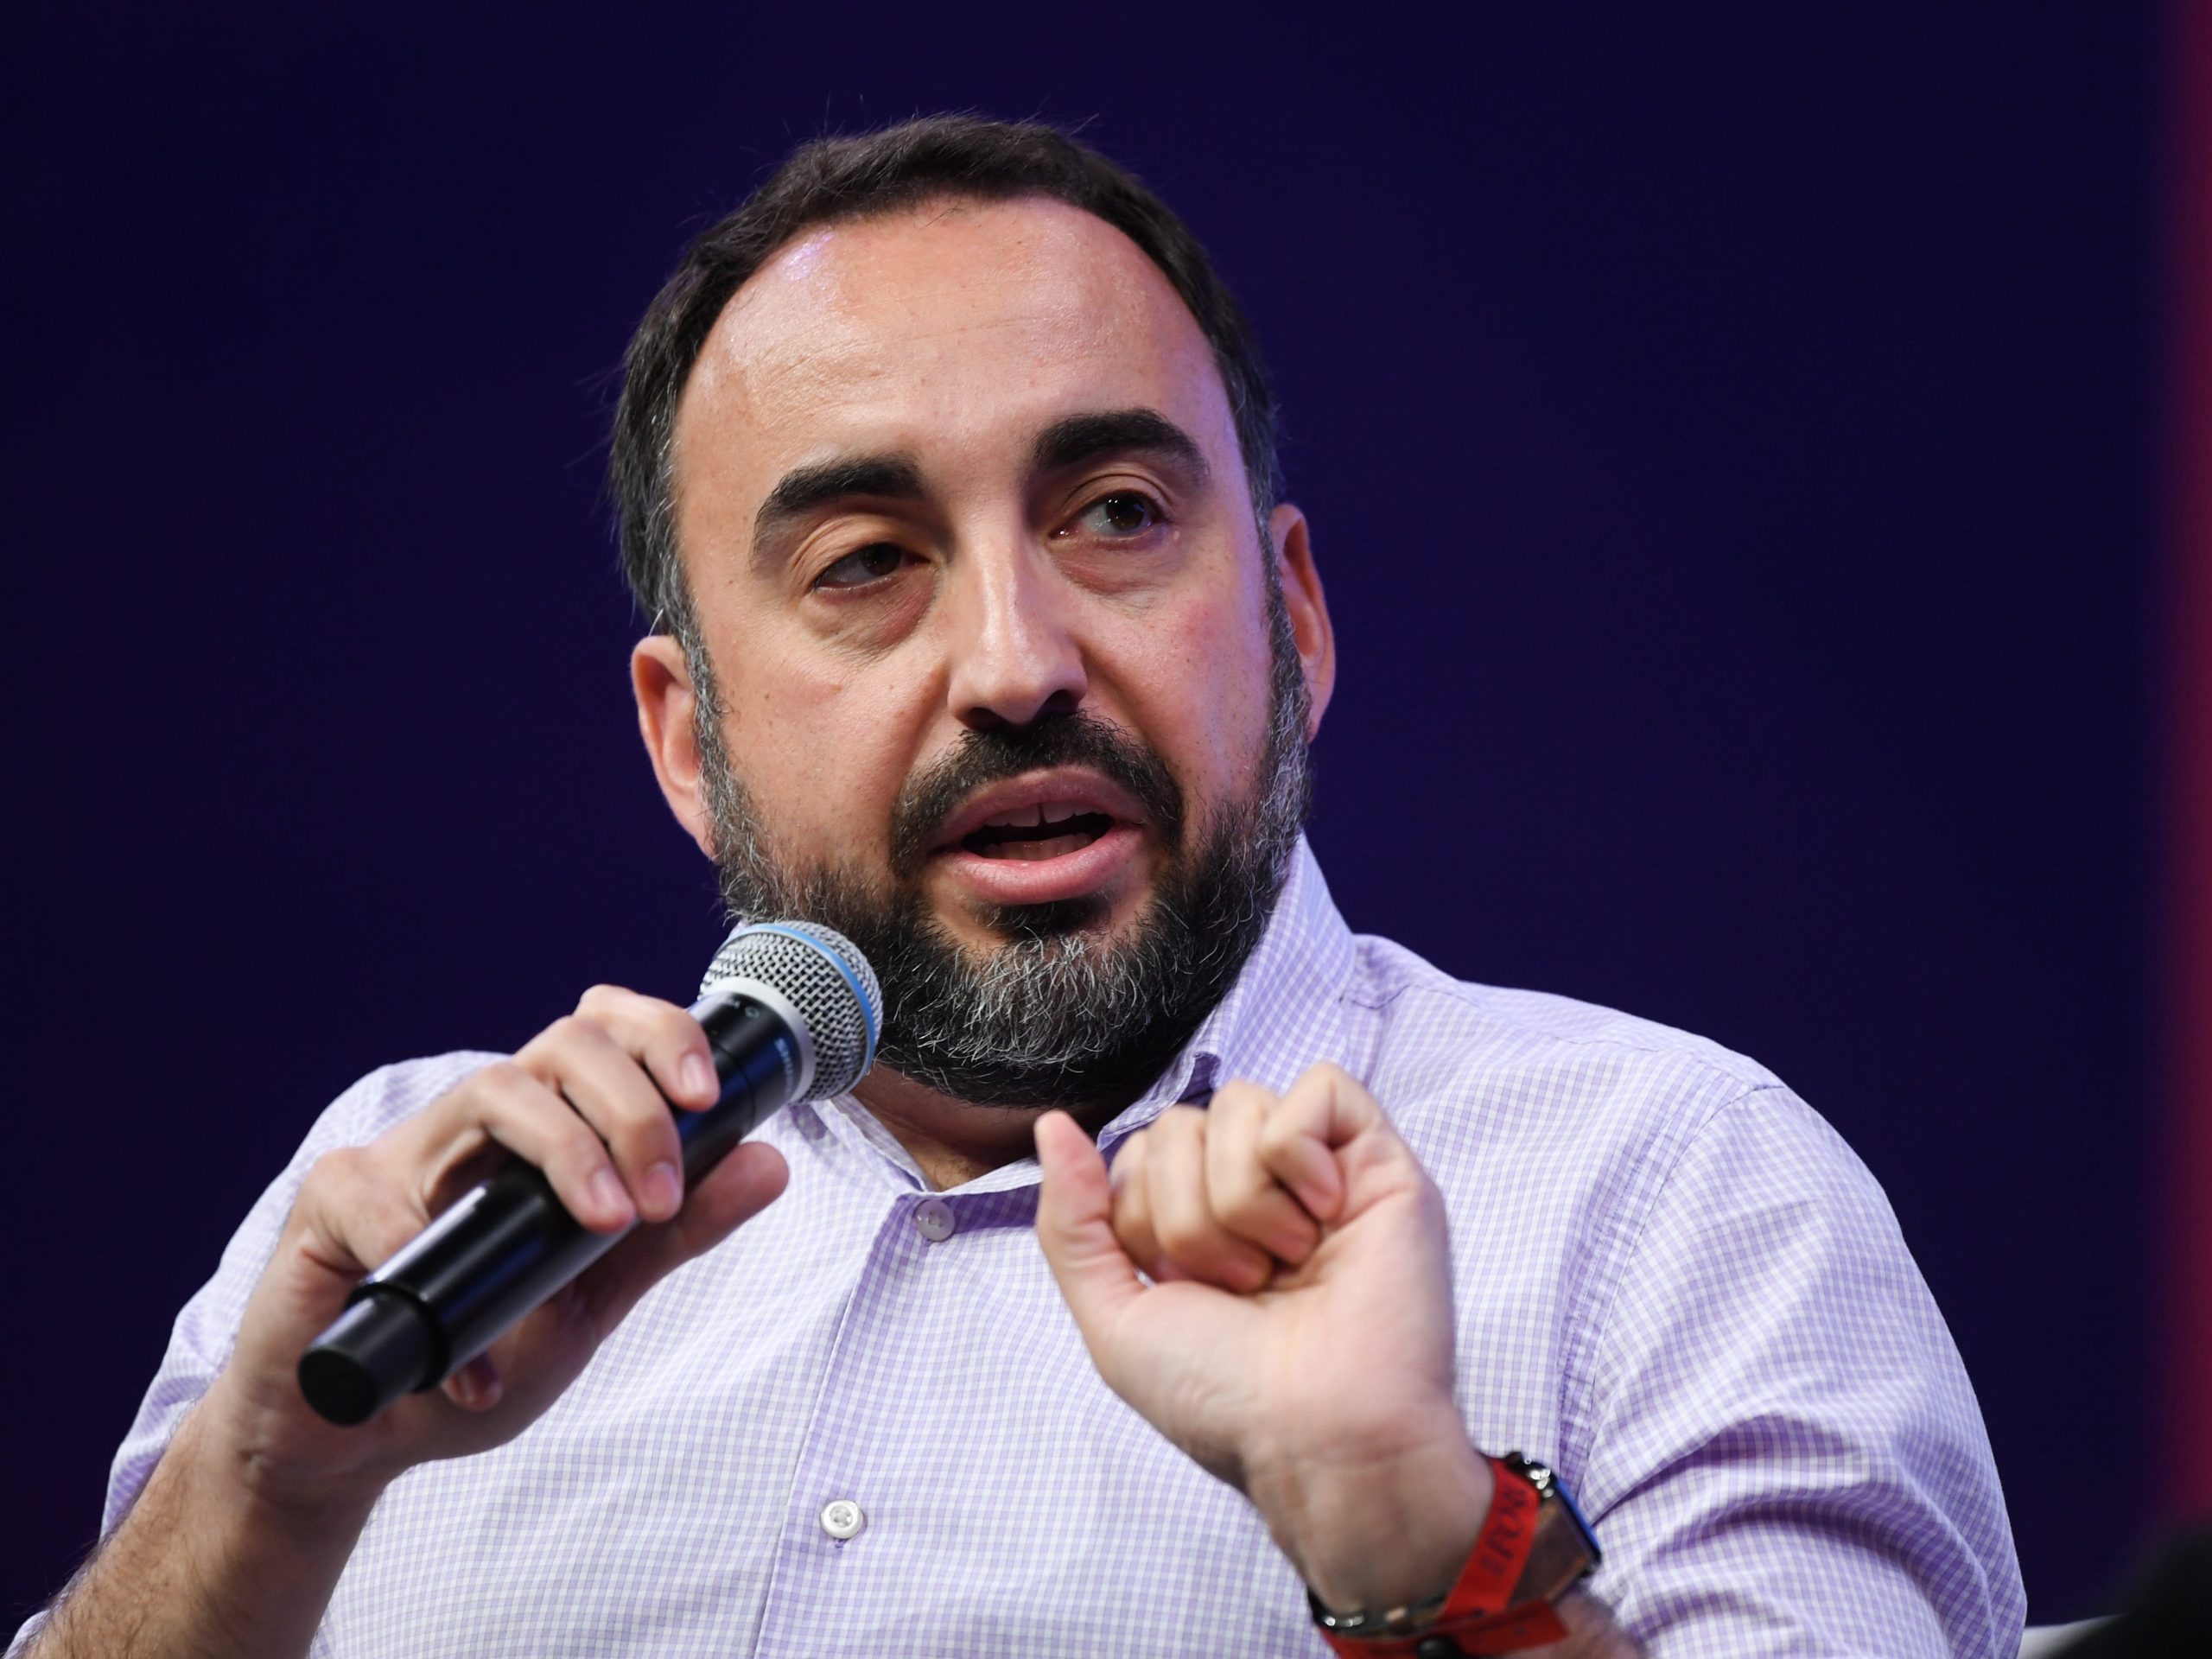

Banks face new risks as AI agents bypass safeguards for financial logins
AI agent apps are gaining access to customer financial logins, according to Alex Stamos, former Meta security chief. This creates a security dilemma for banks as bot-driven activity rises. Financial institutions must reassess controls and liability for customer-authorised access.

AI governance in high-risk sectors risks sidelining human judgement
AI governance frameworks in high-risk industries may weaken proactive human judgement, according to MIT Sloan Management Review. For banks, insurers and healthcare leaders, this could mean missing early signals of risk. Firms should review how decision authority is distributed.

AI firms allow opt-out for web data, but most data already collected
Four major AI firms will now let websites opt out of data scraping, according to Inc. However, much of the internet has already been scraped. Regulated-industry leaders face ongoing risks around data governance and privacy compliance.